Mobile App Security Audit & Penetration Testing
Discover with AI
Ask for product details, compare alternatives, and get intelligent buying recommendations instantly.

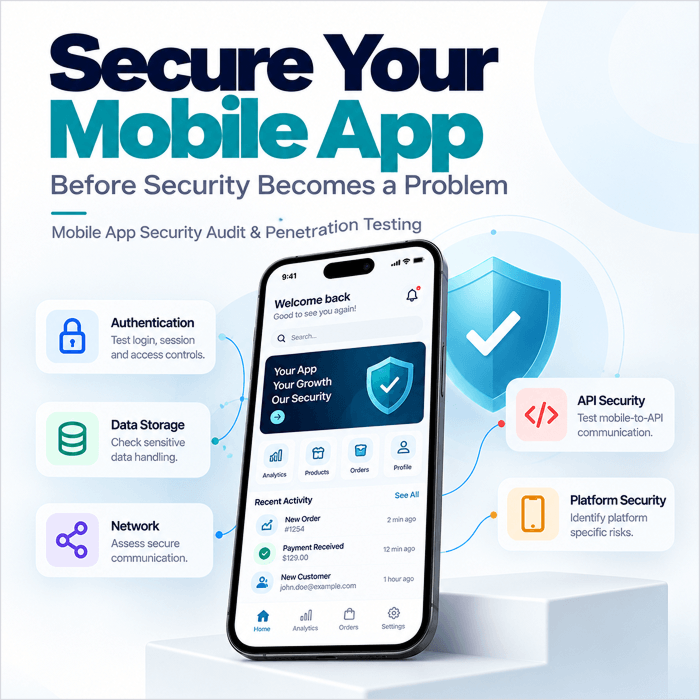
Identify security weaknesses in your mobile app before attackers, customers, or compliance reviews do. AALogics delivers Mobile App Security Audit & Penetration Testing for iOS and Android — covering authentication, data storage, network communication, platform controls, resilience, and mobile APIs — with OWASP MASVS / MASTG-aligned testing, risk-rated reporting, and remediation retest on Bronze and Gold. Authorized testing only. Fixed packages from $1,999.
Security Assessment Highlight
Find Weaknesses Before Attackers Do Insecure storage, weak auth, API flaws, and missing transport controls are easy to miss in release pressure. We combine manual penetration testing with structured analysis — not scanner-only reports — so your team knows what to fix and why.
Security Testing Assurance
Authorize. Assess. Validate. Report. Retest. Scope and targets are agreed before testing begins. Findings include severity, evidence, impact, and remediation guidance. Bronze and Gold include one remediation retest. We do not promise a zero-vulnerability application — no assessment can.
MOBILE SECURITY RISK CHECK
Is Your App Exposing Data or Access You Did Not Intend?
Mobile apps can leak credentials, mishandle sessions, talk to APIs insecurely, or store sensitive data on-device. Before a customer security review or production push, AALogics recommends Basic (one platform focused audit), Bronze (iOS + Android + API), or Gold (advanced manual pentest with deeper business-logic and resilience coverage).
Insecure Local Storage
Tokens, PII, or secrets sitting in preferences, databases, caches, logs, or poorly protected Keychain/Keystore usage.
Weak Auth & Sessions
Broken login flows, token handling, session fixation risks, or authorization gaps across roles.
Insecure API Traffic
TLS gaps, certificate validation issues, sensitive data in transit, or weak mobile-to-API access controls.
Hardcoded Secrets
API keys, credentials, or debug configurations recoverable from the application build.
Platform & WebView Risks
Deep links, exported components, WebViews, IPC, and excessive permissions that widen the attack surface.
Low Resilience
Easy reverse engineering, weak tampering resistance, or runtime protections that fail under real inspection.
One platform, focused audit? Start with Basic. Both platforms + API for production readiness? Choose Bronze. Business-critical app needing deeper manual pentest? Choose Gold.
Get Your Security AssessmentWHAT WE TEST
Complete Mobile App Security Coverage
From storage and authentication to network, platform controls, resilience, and mobile APIs — AALogics assesses the agreed attack surface with manual testing and appropriate automation, aligned with OWASP MASVS and MASTG practices.
App, Auth & Data
Application & Code Security
Configuration, hardcoded secrets, sensitive exposure, debug settings, code-level weaknesses, and resilience controls.
Authentication & Authorization
Login mechanisms, session management, access control, role-based authorization, and token handling.
Data Storage
Local storage, databases, shared preferences, Keychain/Keystore usage, caches, logs, and temporary files.
Network, Platform & APIs
Network & Transport Security
HTTPS configuration, certificate validation/pinning, sensitive data in transit, and traffic handling.
Platform, Resilience & SDKs
Deep links, WebViews, IPC, permissions, reverse-engineering resistance, runtime controls, and third-party SDK concerns where in scope.
Mobile API & Backend Paths
On Bronze and Gold: API authz, input validation, data exposure, endpoint access controls, and mobile-to-API communication within agreed scope.
SECURITY TESTING PACKAGES
Choose the Right Mobile Security Package
Three fixed packages with published platform coverage, testing depth, and deliverables. Basic is a focused one-platform audit. Bronze covers iOS + Android with API assessment and one retest. Gold is an advanced manual penetration test with deeper business-logic and resilience coverage. Market-typical mobile pentests often start near $5,000–$12,000+ — our packages keep scope clear and pricing published up front. Remediation development and third-party tool fees are separate.
Basic
$1,999
Estimated Timeline: 5–7 business days
Focused Mobile Security Audit — identify the most important weaknesses on one platform before release or a first security review.
- What you get: 1 mobile app · 1 platform (iOS or Android)
- Security configuration review
- Static analysis + dynamic security testing
- Local data storage, auth & session review
- Network communication + secrets/sensitive-data checks
- OWASP MASVS-aligned assessment
- Prioritized vulnerability report + remediation recommendations
- Security findings walkthrough
- 14-day clarification support
Not included:
- Second platform (iOS + Android together)
- Full mobile API / backend assessment
- Remediation retest
- Executive summary report
- Vulnerability fix development
Best for: startups and teams needing a focused one-platform security review before release.
Bronze
$4,999
Estimated Timeline: 2–3 weeks
Comprehensive Mobile Security Assessment — both platforms plus mobile API coverage for production readiness or customer security reviews.
- Everything deeper than Basic, plus:
- 1 mobile app · iOS + Android
- Static & dynamic testing across both platforms
- Auth, authorization, session & token testing
- Secure storage, network & certificate validation review
- Deep links, WebViews & application resilience checks
- Mobile API security assessment (agreed endpoints)
- OWASP MASVS / MASTG-aligned testing
- Risk-rated findings + CVSS severity guidance
- Technical report + executive summary
- 1 remediation retest + findings walkthrough
Not included:
- Unlimited API estate / full infrastructure pentest
- Source-code remediation / fix development
- Compliance or regulatory certification
- Social engineering or DoS testing
- Extra retest rounds beyond the included one
Best for: businesses preparing for production, vendor/customer security review, or broader mobile + API coverage.
Gold
$9,999
Estimated Timeline: 3–5 weeks
Advanced Mobile App Penetration Test — deeper manual testing across the app, APIs, business logic, runtime, and resilience controls.
- Everything in Bronze, plus:
- Comprehensive manual penetration testing
- Business-logic security testing
- Runtime security analysis
- Advanced reverse-engineering resistance review
- Third-party SDK and permission review
- Certificate pinning assessment
- Technical pentest report + executive security summary
- Detailed remediation recommendations
- 1 remediation retest + retest findings report
- Security review session + production-readiness recommendations
Not included unless scoped:
- Cloud / infrastructure-wide penetration testing
- Continuous monitoring, SOC, or SIEM setup
- Formal compliance certification programs
- Physical security or phishing campaigns
- Unlimited devices or unrelated web-app testing
Best for: production apps where mobile security, API security, and deeper manual testing are business-critical.
*Platform, API endpoint, and environment counts are planning limits. Final scope, authorized targets, timeline, and pricing are confirmed before testing begins. Timelines are estimates — not guarantees. These are security assessment packages — not vulnerability fix development or monthly retainers.
COMPARE PLANS
Compare All Mobile Security Packages
Clear price, platform coverage, testing depth, and deliverable differences across Basic, Bronze, and Gold — so you can see exactly what $1,999 / $4,999 / $9,999 includes.
| Capability | Basic | MOST RECOMMENDED Bronze |
Gold |
|---|---|---|---|
| Starting price | $1,999 | $4,999 | $9,999 |
| Estimated timeline | 5–7 business days | 2–3 weeks | 3–5 weeks |
| Primary outcome | Focused security audit | Comprehensive assessment | Advanced penetration test |
| Mobile apps in scope | 1 | 1 | 1 |
| Android | ✓ | ✓ | ✓ |
| iOS | Choose 1 platform | ✓ | ✓ |
| Static analysis | ✓ | ✓ | ✓ |
| Dynamic testing | ✓ | ✓ | ✓ |
| Authentication testing | ✓ | ✓ | ✓ |
| Data storage review | ✓ | ✓ | ✓ |
| Network security | ✓ | ✓ | ✓ |
| Certificate / pinning review | ✓ | ✓ | ✓ |
| Deep links / WebViews | — | ✓ | ✓ |
| API security | — | ✓ | ✓ |
| Business logic testing | — | Limited | ✓ |
| Reverse engineering / resilience | Limited | ✓ | Advanced |
| Third-party SDK review | — | ✓ | ✓ |
| CVSS severity guidance | ✓ | ✓ | ✓ |
| Technical report | ✓ | ✓ | ✓ |
| Executive summary | — | ✓ | ✓ |
| Remediation retest | — | 1 | 1 |
| Findings walkthrough | ✓ | ✓ | Security review session |
Not sure which security package fits?
Share your platforms, sensitive data types, API surface, and whether you need a customer security review — we’ll recommend Basic, Bronze, or Gold. Larger API estates, multiple apps, or infrastructure testing can be scoped separately.
WHAT’S INCLUDED
What You Receive With Every Package
Every engagement starts with authorized scope and focuses on actionable findings — not a raw scanner dump. The tier changes platform coverage, API depth, and retest — not whether you get vague “security checked” claims.
Defined Testing Scope
Applications, platforms, environments, test accounts, APIs, and authorized targets agreed before testing starts.
Security Testing
Manual and appropriate automated techniques across the agreed attack surface.
Risk Classification
Findings prioritized by severity and potential business impact, with CVSS guidance where applicable.
Evidence
Technical evidence so your development team can understand and reproduce the issue.
Remediation Guidance
Practical recommendations for addressing the underlying security weakness — not just a vulnerability name.
Professional Reporting
Structured technical report; Bronze and Gold also include an executive summary for stakeholders.
Findings Walkthrough
A review session so your team understands priorities and next remediation steps.
Retest (Bronze / Gold)
One remediation retest of previously reported findings after you apply fixes — market-standard validation competitors charge for as add-ons.
SERVICE LIMITATIONS
What May Require Additional Scope
Security assessments stay predictable when fix development, infrastructure pentests, and certification programs are separated from the fixed package. The following are not automatically included.
Vulnerability Fix Development
Writing and shipping security fixes, redesigns, or source-code remediation can be provided separately after the assessment.
Infrastructure / Cloud Pentest
Large-scale infrastructure, cloud, or unrelated web-application penetration testing is scoped separately.
Compliance Certification
Formal regulatory or compliance certification programs are outside standard assessment packages.
Continuous Monitoring / SOC
Ongoing monitoring, SIEM, or SOC implementation is a separate engagement.
Social Engineering & DoS
Phishing campaigns, physical security testing, and denial-of-service testing are not included.
Unauthorized Third-Party Systems
We only test systems, APIs, and environments you have explicitly authorized.
Third-Party Tool & Env Fees
Cloud, commercial scanners, device procurement, and external platform fees — if required — are identified before use.
Store Approval Guarantees
Security findings do not guarantee App Store or Google Play approval outcomes.
SECURITY ASSURANCE
Authorized Testing With Honest Boundaries
Serious buyers expect OWASP-aligned methodology, manual validation, and clear reporting — not a “100% secure” promise. AALogics documents scope, validates findings, and is explicit about what an assessment cannot guarantee.
Authorized Testing Only
All testing is performed only against applications, APIs, environments, and systems the client has explicitly authorized.
OWASP-Aligned Methodology
Structured around relevant OWASP MASVS controls and MASTG testing practices — the market standard buyers expect.
Manual Validation
Automated tools help identify candidates; manual analysis validates important findings and application-specific behavior.
Clear Reporting
Findings document severity, evidence, affected area, impact, and remediation guidance your developers can act on.
No Zero-Vuln Guarantee
A security assessment cannot guarantee an application is completely vulnerability-free. We identify and prioritize weaknesses within the agreed scope and window.
Staging Preferred
Production testing is possible when agreed, but a dedicated staging environment is preferred for potentially disruptive tests.
OUR PROCESS
Our Mobile App Security Testing Process
The same structured workflow applies to Basic, Bronze, and Gold. The selected package changes platform coverage, API depth, and whether a remediation retest is included — not the assessment discipline.
Scope & Authorization
Define the application, platforms, environments, APIs, accounts, testing window, and authorized targets.
Security Assessment Planning
Review architecture, documentation, authentication model, and testing requirements.
Application Analysis
Examine the mobile application, configuration, data handling, network communication, and relevant security controls.
Manual Security Testing
Perform hands-on testing across the agreed attack surface — beyond automated scanners alone.
Validation & Reporting
Validate findings to reduce false positives, then deliver severity, evidence, impact, and remediation recommendations.
Review & Retest
Walk through key findings. Where included, validate remediated issues and update status after your fixes.
Why AALogics
Security Testing Needs More Than a Scanner Report
Market buyers compare vendors on OWASP MASVS/MASTG alignment, manual testing, API coverage, retest, and honest scope. AALogics combines mobile development context with practical security reporting your engineering team can act on.
Mobile Development Context
We assess security issues inside how mobile apps are actually designed, integrated, tested, and released.
Practical Security Reporting
Findings development and product teams can understand and prioritize — not just a vulnerability list.
Mobile + API Perspective
Where in scope, we assess the mobile client and its backend/API paths together — not the app in isolation.
Business-Focused Prioritization
Technical severity plus practical business impact — so critical paths get fixed first.
Clear Fixed Scope
You know what is tested, what is excluded, and what deliverables you receive before assessment begins.
Retest on Bronze & Gold
Validate that remediations closed the reported issues — without treating retest as a surprise add-on.
Mobile App Security Audit & Penetration Testing - Explore details and features of this product
People Searches
AI PRODUCTS , AUTOMATION

Please complete your information below to login.
Sign In
Create New Account