Magento 2 Malware Removal Service
Discover with AI
Ask for product details, compare alternatives, and get intelligent buying recommendations instantly.

Is your Magento Store is hacked or infected with Malware virus? Contact us for the malware removal process and receive a free consultation and stay secure.
Store Currently Compromised?
Malware costs Magento merchants average $4k/day in lost sales and results in immediate Google blacklisting. Our emergency response team initiates cleanup immediately.
100% Hack-Free Guarantee
If your store experiences any security issues within 30 days post-cleanup, our team will re-intervene completely free of charge.
MAGENTO SYMPTOMS AUDIT
Is Your Magento Store Showing Any of These Signs?
Compromised stores rarely shout. Instead, silent skimmers steal credit cards, manipulate checkout flows, and inject server backdoors without disrupting normal traffic.
Unexpected Customer Redirects
Customers are redirected to spam sites, fake search engines, or copycat checkouts during their checkout flow.
Google & Browser Warnings
Visitors receive immediate warning prompts with red background screens labeling your store as containing harmful software.
Checkout Form Tampering
Standard payment input fields look modified, load with slight lag, or checkout forms fail to process payments on first attempt.
Unknown Admin Accounts
New, unrecognized administrators with generic emails appear overnight in your Magento admin session logs.
Injected Files & Obfuscated Code
Core Magento system hashes do not match vanilla source code. Encrypted PHP eval strings discovered in index.php.
Strange Server Downtime / Errors
Sudden spike in CPU utilization, memory exhaustion, or recurrent administrative panel blockages.
Don't see your exact security threat listed above?
Get an Emergency AssessmentWHAT WE INSPECT
Complete Magento Security Coverage
We inspect your Magento application, database, extensions, checkout flow and access points to identify malware, backdoors and security risks.
Detection & Cleanup
Deep Malware Scan
Automated scan of all system assets plus historical comparison maps.
File Sanitization & Core Alignment
Vanilla restore of core codebase files, removing malicious modifications.
Database Audit & Skimmer Scans
Checking config_data and core layout tables for injected remote scripts.
Backdoor Discovery & Eradication
Locating rogue web shells, hidden access nodes, and backdoor mechanisms.
Suspicious JS Extraction
Removing script blocks, credit card sniffers, and payment redirection scripts.
Security Patch Audit
Reviewing active Magento Security Patches to identify pending updates.
Hardening & Verification
Vulnerable Extension Quarantine
Identifying and blocking insecure third-party packages or obsolete extensions.
Admin Portal Access Review
Disabling compromised, unused, or suspicious admin credentials.
Strict File System Permissions
Configuring server directory permissions to prevent write actions.
Checkout Integrity Inspection
Simulated sandbox checkouts verifying clean, encrypted payment paths.
Platform Functional QA
Complete functional checks on catalog, shopping cart, and transaction routes.
Vulnerability Post-Audit Report
Detailed breakdown of discovered malware nodes and hardening actions taken.
COMPARE PLANS
Choose the Right Recovery Package
Select the level of malware remediation and security hardening that best fits the severity of your Magento store issue.
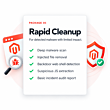
Rapid Cleanup
For detected malware with limited impact
$299
One-time service fee
Response: Next Business Day
Delivery: 3-7 Days
Essential malware cleanup for affected Magento stores.
Get Started- Deep malware scan
- Injected file removal
- Backdoor web shell detection
- Suspicious JS extraction
- Basic incident audit report
- Next business day response
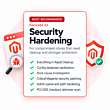
Security Hardening
For compromised stores that need cleanup and stronger protection
$499
One-time service fee
Response: Under 4 Hours
Delivery: 2-3 Days
Best for stores needing cleanup plus patching and hardening.
Get Started- Everything in Rapid Cleanup
- Config database sanitization
- Root-cause investigation
- Critical Magento security patching
- Admin panel & path hardening
- PCI-DSS checkout skimmer scan
- 30-day re-clean assurance
- Under 4 hours priority response
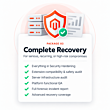
Complete Recovery
For serious, recurring, or high-risk compromises
$1,499
One-time service fee
Response: Immediate
Delivery: 1-3 Days
Full forensic recovery and deeper technical remediation.
Get Started- Everything in Security Hardening
- Extension compatibility & safety audit
- Server infrastructure audit
- Platform functional QA
- Full forensic incident report
- 90-day re-clean assurance
- Immediate response under 2 hours
- Advanced recovery coverage
COMPARE PLANS
Compare All Recovery Plans
See exactly what is included in each Magento malware recovery package so you can choose the right level of protection for your store.
| Capability | Rapid Cleanup For limited-impact infections |
MOST RECOMMENDED Security Hardening For compromised stores |
Complete Recovery For serious or recurring compromises |
|---|---|---|---|
| Detection & Cleanup | |||
| Deep Malware Scan | ✓ | ✓ | ✓ |
| Injected File Removal | ✓ | ✓ | ✓ |
| Suspicious JavaScript Removal | ✓ | ✓ | ✓ |
| Backdoor Detection | ✓ | ✓ | ✓ |
| Database Sanitization | — | ✓ | ✓ |
| Root Cause & Hardening | |||
| Root-Cause Investigation | — | ✓ | ✓ |
| Magento Security Patch Review | — | ✓ | ✓ |
| Admin Access Hardening | — | ✓ | ✓ |
| File Permission Review | — | ✓ | ✓ |
| Vulnerable Extension Audit | — | — | ✓ |
| Advanced Security Review | |||
| Checkout Skimmer Inspection | — | — | ✓ |
| Server Infrastructure Audit | — | — | ✓ |
| Extension Compatibility & Safety Audit | — | — | ✓ |
| Platform Functional QA | Basic | Detailed | Full |
| Assurance & Support | |||
| Incident Report | Basic | Detailed | Full Forensic |
| Post-Cleanup Monitoring | — | 30 Days | 90 Days |
| Re-Clean Assurance | — | 30 Days | 90 Days |
| Priority Response | Next Business Day | Under 4 Hours | Under 2 Hours |
| Estimated Delivery | 3–7 Days | 2–3 Days | 1–3 Days |
Not sure which plan fits your store?
Tell us what happened and we'll help you choose the right recovery level.
SERVICE LIMITATIONS
What's Included - and What May Require Additional Scope
To keep the recovery process transparent, some issues may require additional investigation, custom work, or third-party coordination depending on the severity of the compromise.
Custom Extension Redevelopment
Repairing or rebuilding deeply compromised third-party or custom extensions is not included unless specified.
Blacklist Removal Approval
We can assist with cleanup and resubmission, but final approval depends on Google or other external security services.
Server Infrastructure Rebuilds
Operating system recovery, full server reconstruction, or hosting migration may require separate scope.
Large Custom Code Repairs
Custom code issues unrelated to malware cleanup may be quoted separately.
Third-Party Account Recovery
Recovery of hosting, payment gateway, email, CDN, or marketplace accounts must be handled with the respective provider.
Timeline Variations
Large stores, severe infections, limited access, or complex integrations may extend estimated delivery time.
RECOVERY ASSURANCE
Safe, Predictable, and Assured Recovery
Our Magento malware recovery service is designed to reduce risk, protect store continuity, and give you confidence throughout the cleanup process.
100% Hack-Free Re-Clean Assurance
If the same malware issue returns within the support window, our team will re-investigate and clean it again per the package scope.
Backup Before Changes
We create a recovery point before major remediation actions to reduce operational risk during cleanup.
Functional Verification
Key storefront flows such as browsing, checkout behavior, and core functionality are reviewed before handover.
Transparent Incident Report
You receive a summary of what was found, what was removed, and what hardening actions were completed.
HOW IT WORKS
Our Magento Recovery Process
We do more than remove malware — we investigate the entry point, secure the environment, and verify the store before handover.
Secure Intake
We collect the incident details and confirm the package or required scope.
Backup
A restore point is created before remediation work begins.
Deep Scan
Files, database, extensions, and suspicious code are investigated.
Malware Removal
Malicious scripts, injected files, and backdoors are removed.
Root-Cause Investigation
We identify the likely source of compromise, such as outdated code, insecure extensions, or unauthorized access.
Security Hardening
We apply agreed hardening actions such as patch reviews, access review, and permission tightening.
Verification
Checkout, catalog, key pages, and store functionality are tested.
Handover
We provide a summary of findings, completed actions, and next recommendations.
Why AAlogics
Magento Security Requires Magento Expertise
When a store is compromised, you need more than general support — you need Magento-focused recovery handled with speed, clarity, and technical discipline.
Magento Specialists
Work with a team experienced in Magento 2 and Adobe Commerce environments.
Secure Incident Handling
We follow a structured recovery approach with controlled access and staged remediation.
Application + Server Awareness
Our investigation considers the Magento application, integrations, and broader environment.
Business Continuity Focus
The goal is not just cleanup — it is restoring a safe, functional commerce operation.
Magento 2 Malware Removal Service - Explore details and features of this product


People Searches
AI PRODUCTS , AUTOMATION

Please complete your information below to login.
Sign In
Create New Account